
Operational views
Review work, evidence, exceptions and authorised decisions within a defined operating scope.
Banking & financial services / APPLICATION BLUEPRINT
Routes screening-provider matches to authorised sanctions specialists for review.
11 workspace menus · 9 business workflows · 5 role profiles
Application blueprint only. This is a proposed design, not a deployed or production-tested system. Screens and sample figures are illustrative; workflows, business rules, approvals, permissions and integrations require confirmation before build.
Designed for operations analysts and the responsible business owners
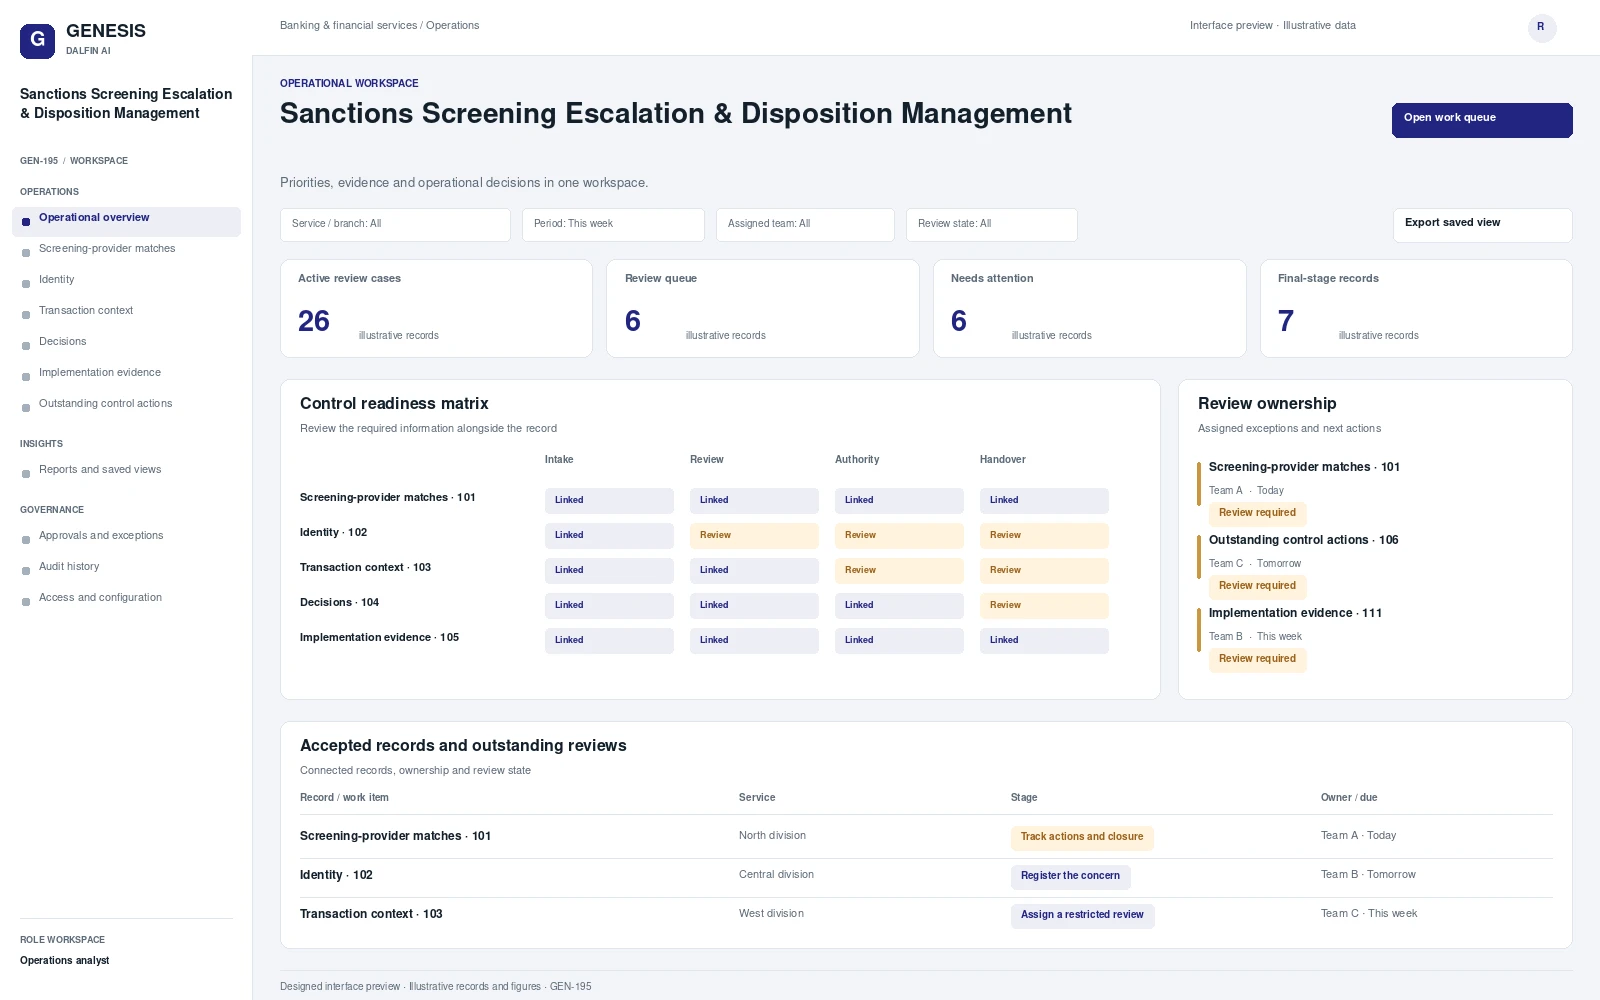
Illustrative workspace and record review. Select a concept screen to inspect it in full.
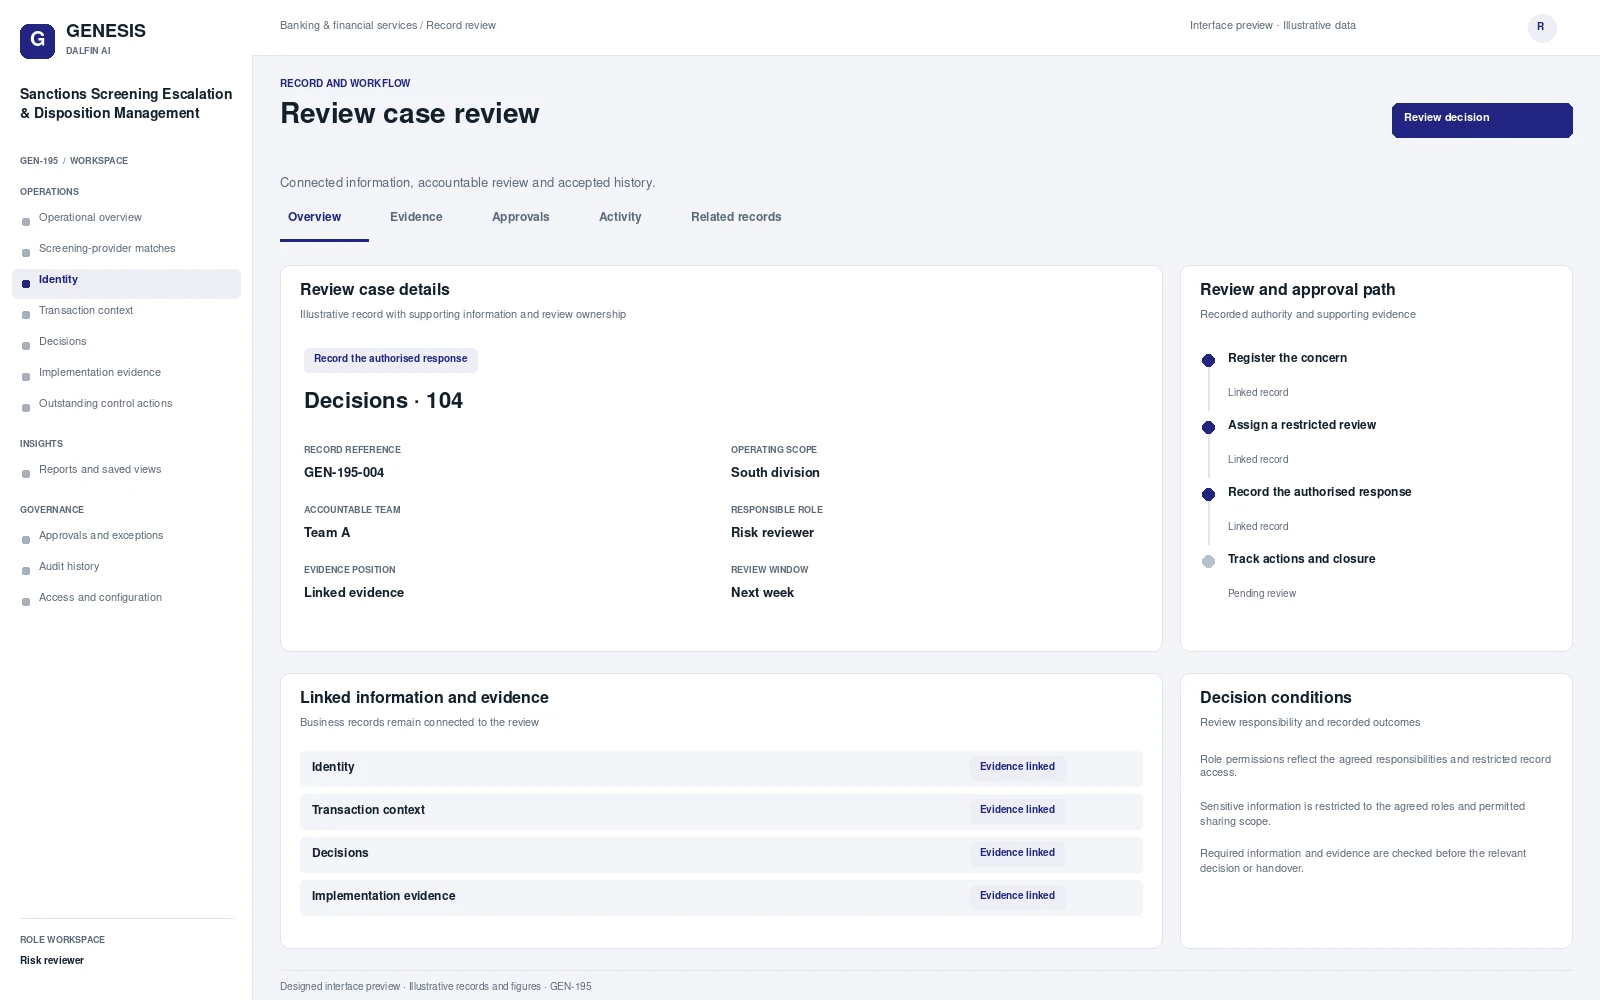
Review work, evidence, exceptions and authorised decisions within a defined operating scope.
Routes screening-provider matches to authorised sanctions specialists for review. Collects identity and transaction context, records decisions and implementation evidence, and tracks outstanding control actions, without independently determining sanctions status or overriding specialist assessments.
From intake to authorised completion, with evidence at each decision.
Establish the scope of screening-provider matches, capture the required records and assign the accountable team.
Coordinate identity, transaction context, with linked evidence and visible outstanding actions.
Review the relevant conditions and exceptions. Record the authorised outcome and its supporting evidence.
Confirm the resulting records and handovers. Track remaining obligations, later changes and follow-up actions.
Select a workflow to review the steps, responsibilities, approval and exception handling.
Coordinate screening-provider matches within Sanctions Screening Escalation and Disposition Management.
Trigger
Screening-provider matches requires a new record, an agreed review or a controlled change.
Responsible role
Operations analyst
Approval
Authorised decision maker records the decision when the action changes an accepted commitment or requires delegated authority.
Exception handling
Required information or responsibility is missing, or an operating condition changes.
Outcome
A completed operating record with its linked evidence and remaining obligations.
Coordinate identity and transaction context within Sanctions Screening Escalation and Disposition Management.
Trigger
Identity and transaction context requires a new record, an agreed review or a controlled change.
Responsible role
Operations analyst
Approval
Authorised decision maker records the decision when the action changes an accepted commitment or requires delegated authority.
Exception handling
Required information or responsibility is missing, or an operating condition changes.
Outcome
A completed operating record with its linked evidence and remaining obligations.
Coordinate decisions and implementation evidence within Sanctions Screening Escalation and Disposition Management.
Trigger
Decisions and implementation evidence requires a new record, an agreed review or a controlled change.
Responsible role
Risk reviewer
Approval
Authorised decision maker records the decision when the action changes an accepted commitment or requires delegated authority.
Exception handling
Evidence is incomplete, disputed, expired or outside the reviewer’s authority.
Outcome
A review finding, its accepted evidence and any accountable corrective actions.
Coordinate outstanding control actions within Sanctions Screening Escalation and Disposition Management.
Trigger
Outstanding control actions requires a new record, an agreed review or a controlled change.
Responsible role
Operations analyst
Approval
Authorised decision maker records the decision when the action changes an accepted commitment or requires delegated authority.
Exception handling
Required information or responsibility is missing, or an operating condition changes.
Outcome
A completed operating record with its linked evidence and remaining obligations.
Coordinate operating requirement within Sanctions Screening Escalation and Disposition Management.
Trigger
Operating requirement requires a new record, an agreed review or a controlled change.
Responsible role
Operations analyst
Approval
Authorised decision maker records the decision when the action changes an accepted commitment or requires delegated authority.
Exception handling
An assumption changes, prerequisites are missing or stakeholders cannot accept the proposed commitment.
Outcome
An approved operating plan and owned actions for its accepted conditions.
Coordinate operating exceptions within Sanctions Screening Escalation and Disposition Management.
Trigger
Operating exceptions requires a new record, an agreed review or a controlled change.
Responsible role
Operations analyst
Approval
Authorised decision maker records the decision when the action changes an accepted commitment or requires delegated authority.
Exception handling
The case exceeds delegation, contains a conflict or has disputed evidence.
Outcome
An authorised decision or escalation with accountable resolution actions.
Coordinate completion and follow-up within Sanctions Screening Escalation and Disposition Management.
Trigger
Completion and follow-up requires a new record, an agreed review or a controlled change.
Responsible role
Risk reviewer
Approval
Authorised decision maker records the decision when the action changes an accepted commitment or requires delegated authority.
Exception handling
Evidence is incomplete, disputed, expired or outside the reviewer’s authority.
Outcome
A review finding, its accepted evidence and any accountable corrective actions.
Coordinate controlled operating changes within Sanctions Screening Escalation and Disposition Management.
Trigger
Controlled operating changes requires a new record, an agreed review or a controlled change.
Responsible role
Risk reviewer
Approval
Authorised decision maker records the decision when the action changes an accepted commitment or requires delegated authority.
Exception handling
Evidence is incomplete, disputed, expired or outside the reviewer’s authority.
Outcome
A review finding, its accepted evidence and any accountable corrective actions.
Coordinate scoped operational reports within Sanctions Screening Escalation and Disposition Management.
Trigger
Scoped operational reports requires a new record, an agreed review or a controlled change.
Responsible role
Operations analyst
Approval
Authorised decision maker records the decision when the action changes an accepted commitment or requires delegated authority.
Exception handling
Required information or responsibility is missing, or an operating condition changes.
Outcome
A completed operating record with its linked evidence and remaining obligations.
Interface scope, data mapping and testing are agreed for each engagement.
Authorised users can review screening-provider matches, supporting records and assigned actions through mobile and tablet access. The relevant tasks and permissions are agreed for the deployment.
Access approved workflows through the Dalfin mobile app. Device tasks and permissions are confirmed for the deployment.
Core workflows and approval rules are defined with your business owners. Operational AI can be assessed separately against a specific business outcome and review requirements.
AI extensions are scoped around the required data, business outcome and review controls.
Connect requirements, roles, records, workflows and interfaces through the agreed Genesis engineering process.
Review dependency impact and validation requirements. Context Memory supports governed changes and accepted application revisions.
Agree customer cloud or on-premises requirements, device access, implementation acceptance and ongoing engineering support.
AN EXAMPLE OPERATING SCENARIO
Start with screening-provider matches and follow the record through assign a restricted review. Introduce a missing item or operating exception, record the authorised resolution and inspect the final handover, evidence and history.
Review a representative review case, its workflow stages, accountable roles, an exception and the resulting operational report. Bring the business process and existing system requirements that matter to your organisation.
The operating scope covers your records, role permissions, review authority, business rules and integration boundaries. These requirements are agreed with the responsible business owners.
Connection design defines interfaces, data ownership, mapping, authentication and exception handling. The agreed implementation includes validation against the selected systems and workflows.
The agreed engineering approach covers review of change impact, bounded implementation, validation and accepted revisions. Discuss the relevant Genesis Context Memory and support requirements during solution scoping.
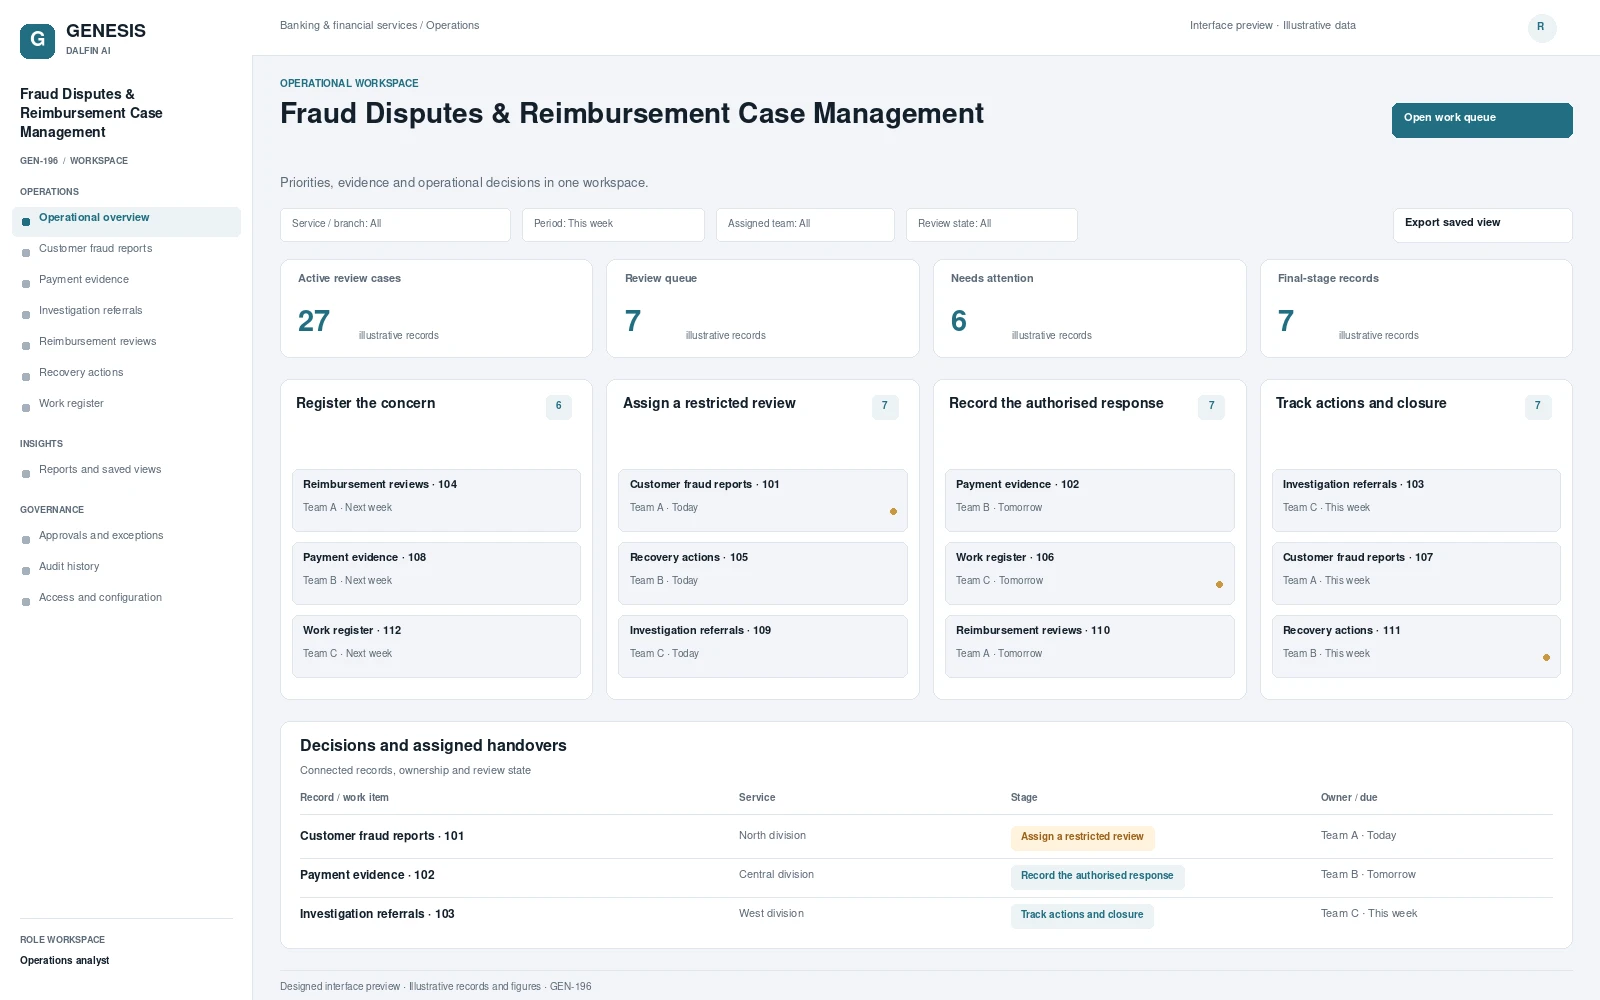 Interface preview
Handles customer fraud reports, payment evidence and investigation referrals.
View blueprint →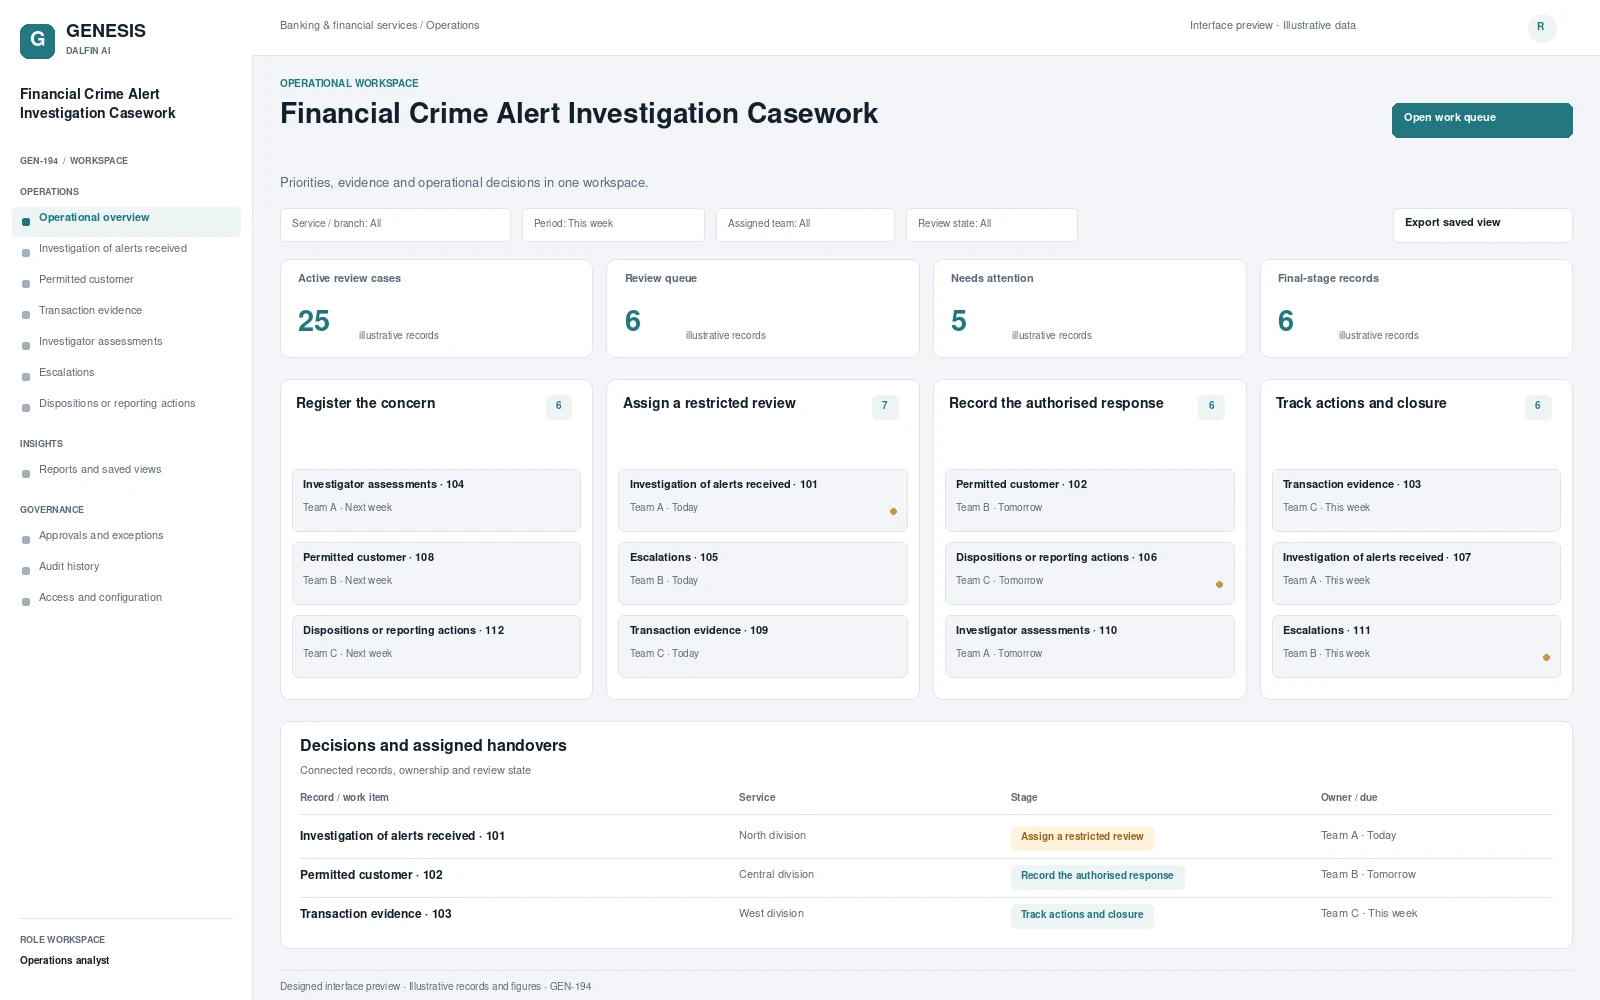 Interface preview
Coordinates investigation of alerts received from approved financial monitoring services.
View blueprint →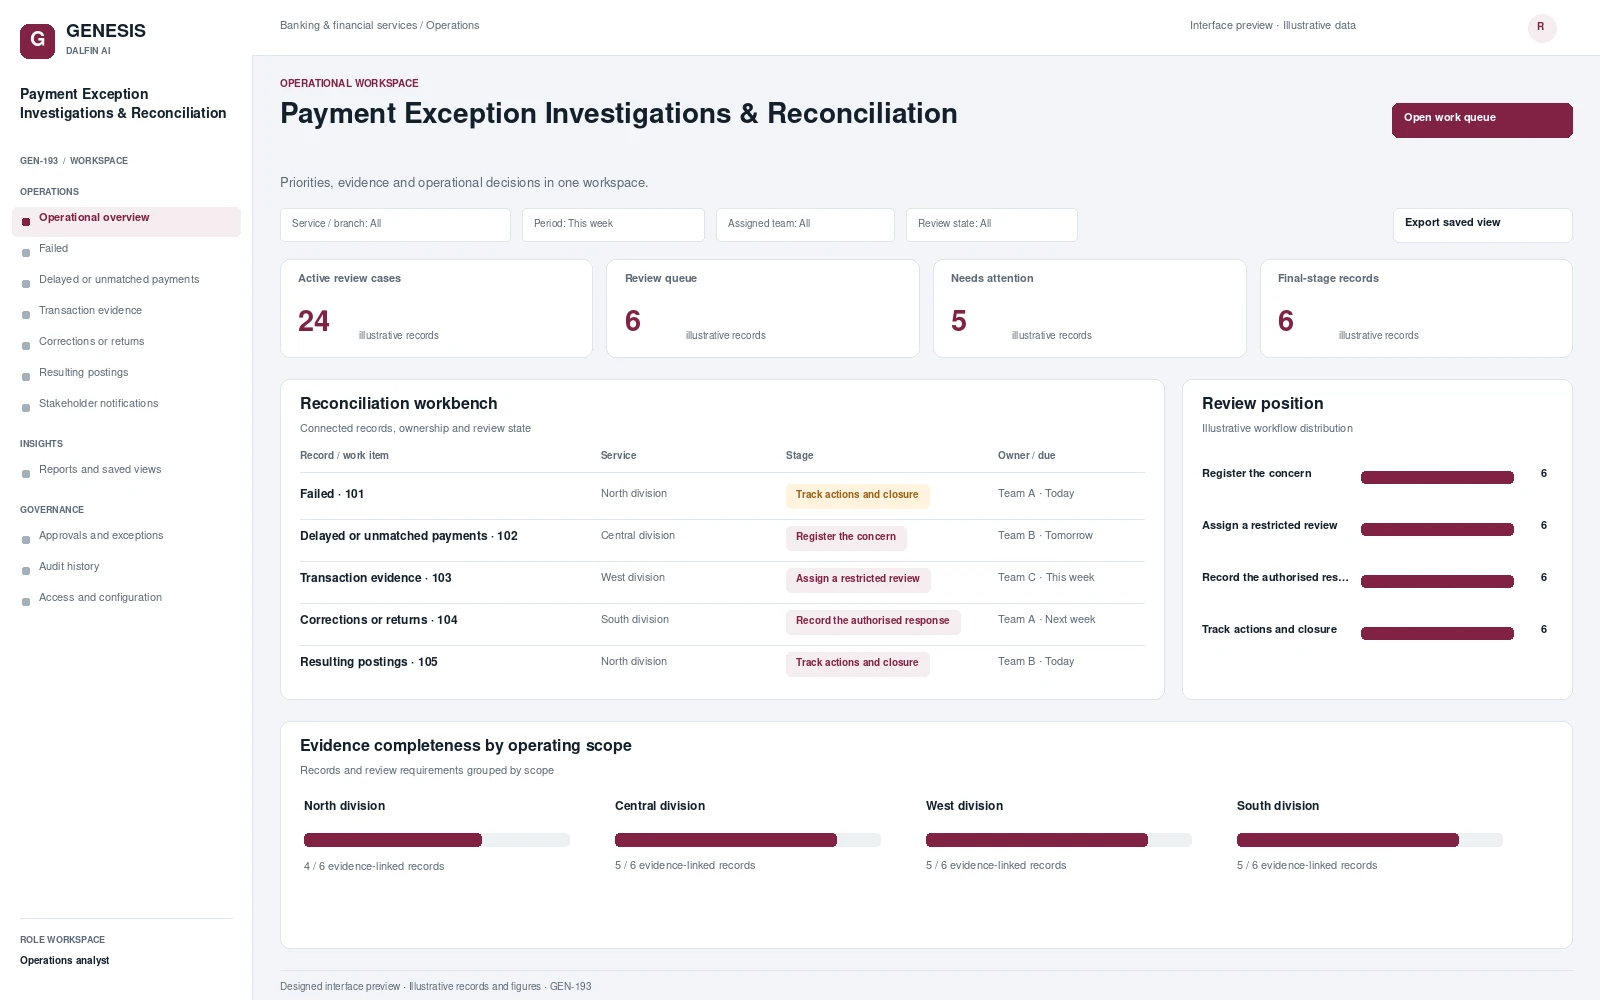 Interface preview
Handles failed, delayed or unmatched payments through investigation queues and supporting transaction evidence.
View blueprint →