
Operational views
Review work, evidence, exceptions and authorised decisions within a defined operating scope.
Enterprise operations / APPLICATION BLUEPRINT
Coordinate validated incident reports, evidence preservation, authorised response actions, restoration review and corrective follow-up.
12 workspace menus · 12 business workflows · 5 role profiles
Application blueprint only. This is a proposed design, not a deployed or production-tested system. Screens and sample figures are illustrative; workflows, business rules, approvals, permissions and integrations require confirmation before build.
Designed for Security operations lead and incident commanders
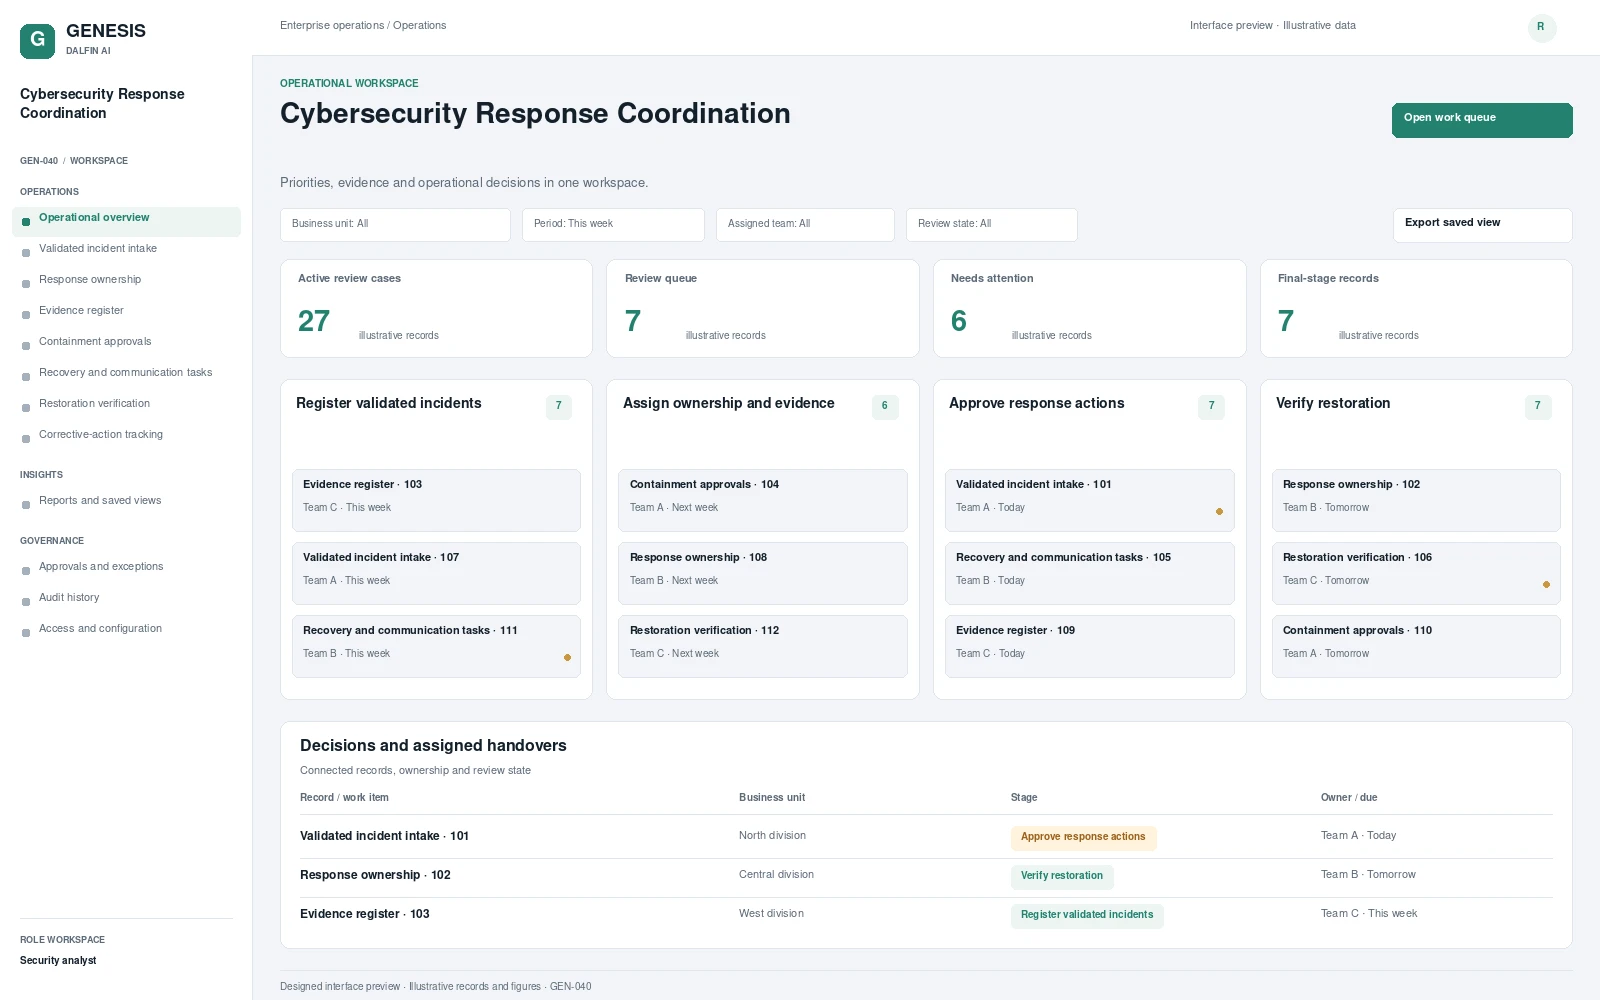
Illustrative workspace and record review. Select a concept screen to inspect it in full.
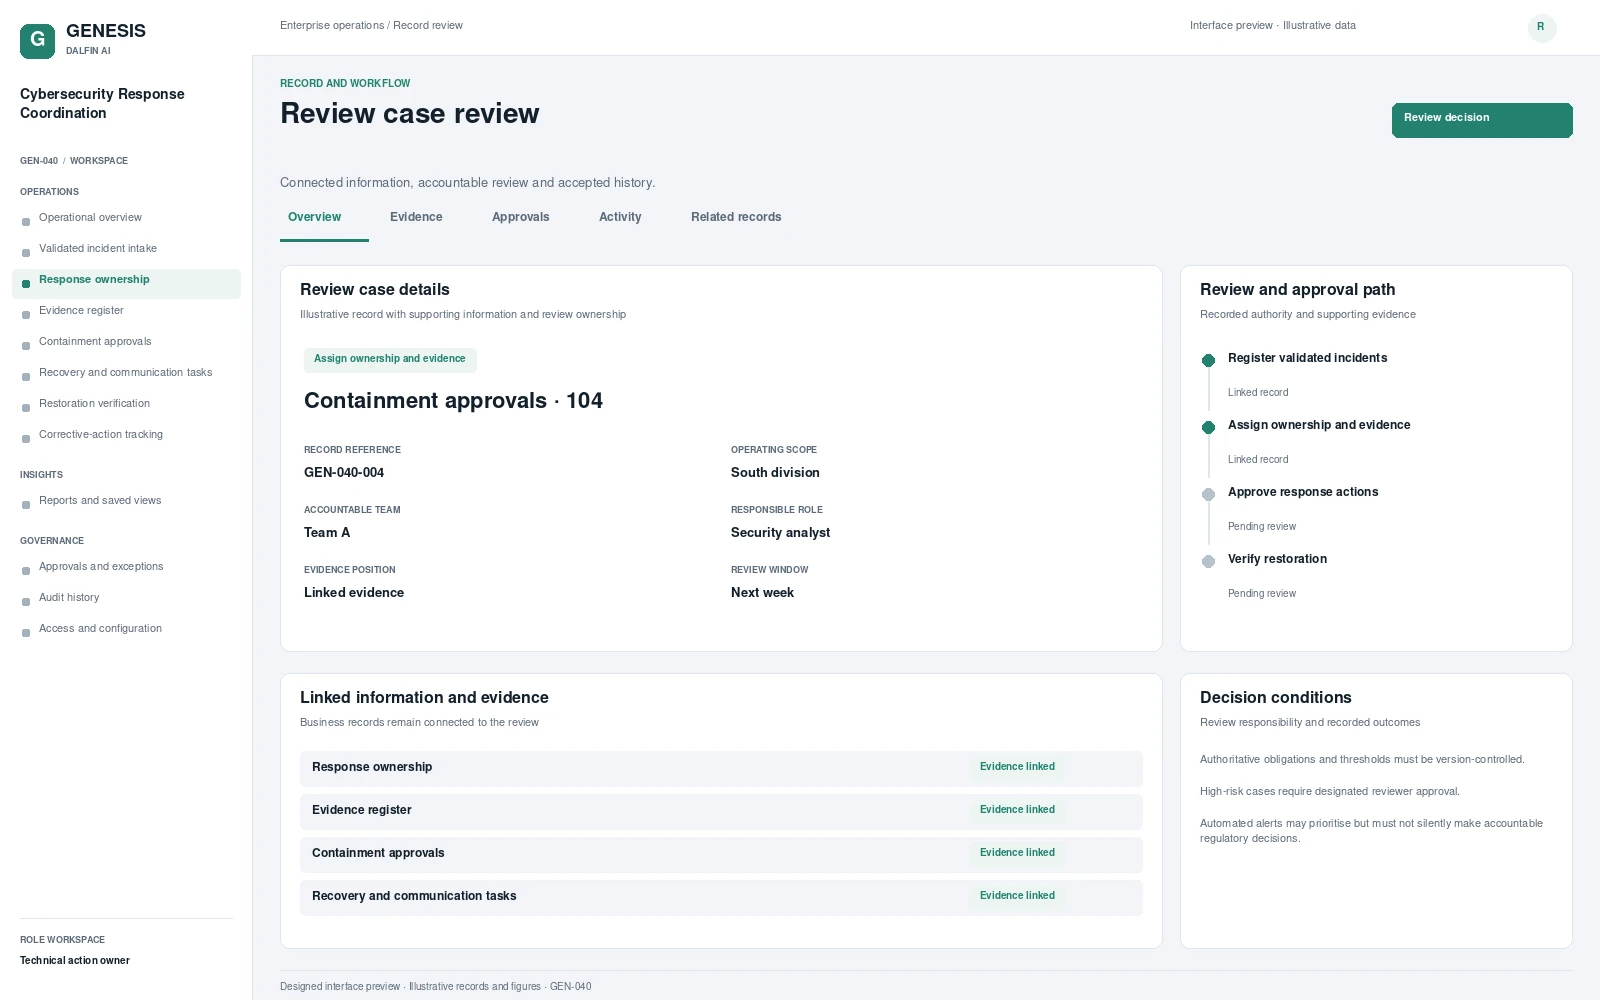
Review work, evidence, exceptions and authorised decisions within a defined operating scope.
Coordinate validated incident reports, evidence preservation, authorised response actions, restoration review and corrective follow-up. During an incident, ownership and approval records can become fragmented across technical tools and communication channels. This administrative scope connects evidence and authorised actions to the response record, preserving who approved containment, recovery and communication before corrective tasks are closed.
From intake to authorised completion, with evidence at each decision.
Receive a validated security alert or incident report.
Assign response ownership and preserve relevant evidence.
Approve containment, recovery and communication actions.
Verify restoration and close corrective follow-up tasks.
Select a workflow to review the steps, responsibilities, approval and exception handling.
Coordinate validated incident intake within Cybersecurity incident response coordination.
Trigger
Validated incident intake requires a new record, an agreed review or a controlled change.
Responsible role
Security analyst
Approval
Communication approver records the decision when the action changes an accepted commitment or requires delegated authority.
Exception handling
Required information or responsibility is missing, or an operating condition changes.
Outcome
A completed operating record with its linked evidence and remaining obligations.
Coordinate response ownership within Cybersecurity incident response coordination.
Trigger
Response ownership requires a new record, an agreed review or a controlled change.
Responsible role
Security analyst
Approval
Communication approver records the decision when the action changes an accepted commitment or requires delegated authority.
Exception handling
Required information or responsibility is missing, or an operating condition changes.
Outcome
A completed operating record with its linked evidence and remaining obligations.
Coordinate evidence register within Cybersecurity incident response coordination.
Trigger
Evidence register requires a new record, an agreed review or a controlled change.
Responsible role
Technical action owner
Approval
Communication approver records the decision when the action changes an accepted commitment or requires delegated authority.
Exception handling
Evidence is incomplete, disputed, expired or outside the reviewer’s authority.
Outcome
A review finding, its accepted evidence and any accountable corrective actions.
Coordinate containment approvals within Cybersecurity incident response coordination.
Trigger
Containment approvals requires a new record, an agreed review or a controlled change.
Responsible role
Security analyst
Approval
Communication approver records the decision when the action changes an accepted commitment or requires delegated authority.
Exception handling
Required information or responsibility is missing, or an operating condition changes.
Outcome
A completed operating record with its linked evidence and remaining obligations.
Coordinate recovery and communication tasks within Cybersecurity incident response coordination.
Trigger
Recovery and communication tasks requires a new record, an agreed review or a controlled change.
Responsible role
Security analyst
Approval
Communication approver records the decision when the action changes an accepted commitment or requires delegated authority.
Exception handling
Content conflicts, missing review or a changed recipient permission prevents release.
Outcome
An accepted content version with distribution and revision history.
Coordinate restoration verification within Cybersecurity incident response coordination.
Trigger
Restoration verification requires a new record, an agreed review or a controlled change.
Responsible role
Security analyst
Approval
Communication approver records the decision when the action changes an accepted commitment or requires delegated authority.
Exception handling
Required information or responsibility is missing, or an operating condition changes.
Outcome
A completed operating record with its linked evidence and remaining obligations.
Coordinate corrective-action tracking within Cybersecurity incident response coordination.
Trigger
Corrective-action tracking requires a new record, an agreed review or a controlled change.
Responsible role
Security analyst
Approval
Communication approver records the decision when the action changes an accepted commitment or requires delegated authority.
Exception handling
Required information or responsibility is missing, or an operating condition changes.
Outcome
A completed operating record with its linked evidence and remaining obligations.
Coordinate operating requirement within Cybersecurity incident response coordination.
Trigger
Operating requirement requires a new record, an agreed review or a controlled change.
Responsible role
Security analyst
Approval
Communication approver records the decision when the action changes an accepted commitment or requires delegated authority.
Exception handling
An assumption changes, prerequisites are missing or stakeholders cannot accept the proposed commitment.
Outcome
An approved operating plan and owned actions for its accepted conditions.
Coordinate operating exceptions within Cybersecurity incident response coordination.
Trigger
Operating exceptions requires a new record, an agreed review or a controlled change.
Responsible role
Security analyst
Approval
Communication approver records the decision when the action changes an accepted commitment or requires delegated authority.
Exception handling
The case exceeds delegation, contains a conflict or has disputed evidence.
Outcome
An authorised decision or escalation with accountable resolution actions.
Coordinate completion and follow-up within Cybersecurity incident response coordination.
Trigger
Completion and follow-up requires a new record, an agreed review or a controlled change.
Responsible role
Technical action owner
Approval
Communication approver records the decision when the action changes an accepted commitment or requires delegated authority.
Exception handling
Evidence is incomplete, disputed, expired or outside the reviewer’s authority.
Outcome
A review finding, its accepted evidence and any accountable corrective actions.
Coordinate controlled operating changes within Cybersecurity incident response coordination.
Trigger
Controlled operating changes requires a new record, an agreed review or a controlled change.
Responsible role
Technical action owner
Approval
Communication approver records the decision when the action changes an accepted commitment or requires delegated authority.
Exception handling
Evidence is incomplete, disputed, expired or outside the reviewer’s authority.
Outcome
A review finding, its accepted evidence and any accountable corrective actions.
Coordinate scoped operational reports within Cybersecurity incident response coordination.
Trigger
Scoped operational reports requires a new record, an agreed review or a controlled change.
Responsible role
Security analyst
Approval
Communication approver records the decision when the action changes an accepted commitment or requires delegated authority.
Exception handling
Required information or responsibility is missing, or an operating condition changes.
Outcome
A completed operating record with its linked evidence and remaining obligations.
Interface scope, data mapping and testing are agreed for each engagement.
Review assigned administrative actions on approved devices. Automated remediation requires separately authorised controls.
Access approved workflows through the Dalfin mobile app. Device tasks and permissions are confirmed for the deployment.
Draft an incident timeline from approved records for commander review.
AI extensions are scoped around the required data, business outcome and review controls.
Connect requirements, roles, records, workflows and interfaces through the agreed Genesis engineering process.
Review dependency impact and validation requirements. Context Memory supports governed changes and accepted application revisions.
Agree customer cloud or on-premises requirements, device access, implementation acceptance and ongoing engineering support.
AN EXAMPLE OPERATING SCENARIO
A validated incident is assigned to a response owner. A containment request requires authorised approval, recovery evidence is reviewed and restoration is verified. The workflow retains the response history and follows outstanding corrective actions to closure.
Roles, approval authority, business rules, records and reporting are configured around your operating model. Scope definition connects the required business outcome to workflows, interfaces and acceptance criteria.
Operators, reviewers and authorised decision makers have defined responsibilities. Approval limits, exception handling and access permissions are agreed with your business owners and tested against the selected workflows.
Interface requirements cover your existing business systems, data ownership, mapping and authentication. Connection design and testing form part of the agreed implementation scope.
Start with a relevant business transaction, then review its approvals, an exception, role permissions and final records. Discuss the integrations, reporting and operating requirements that matter to your organisation.
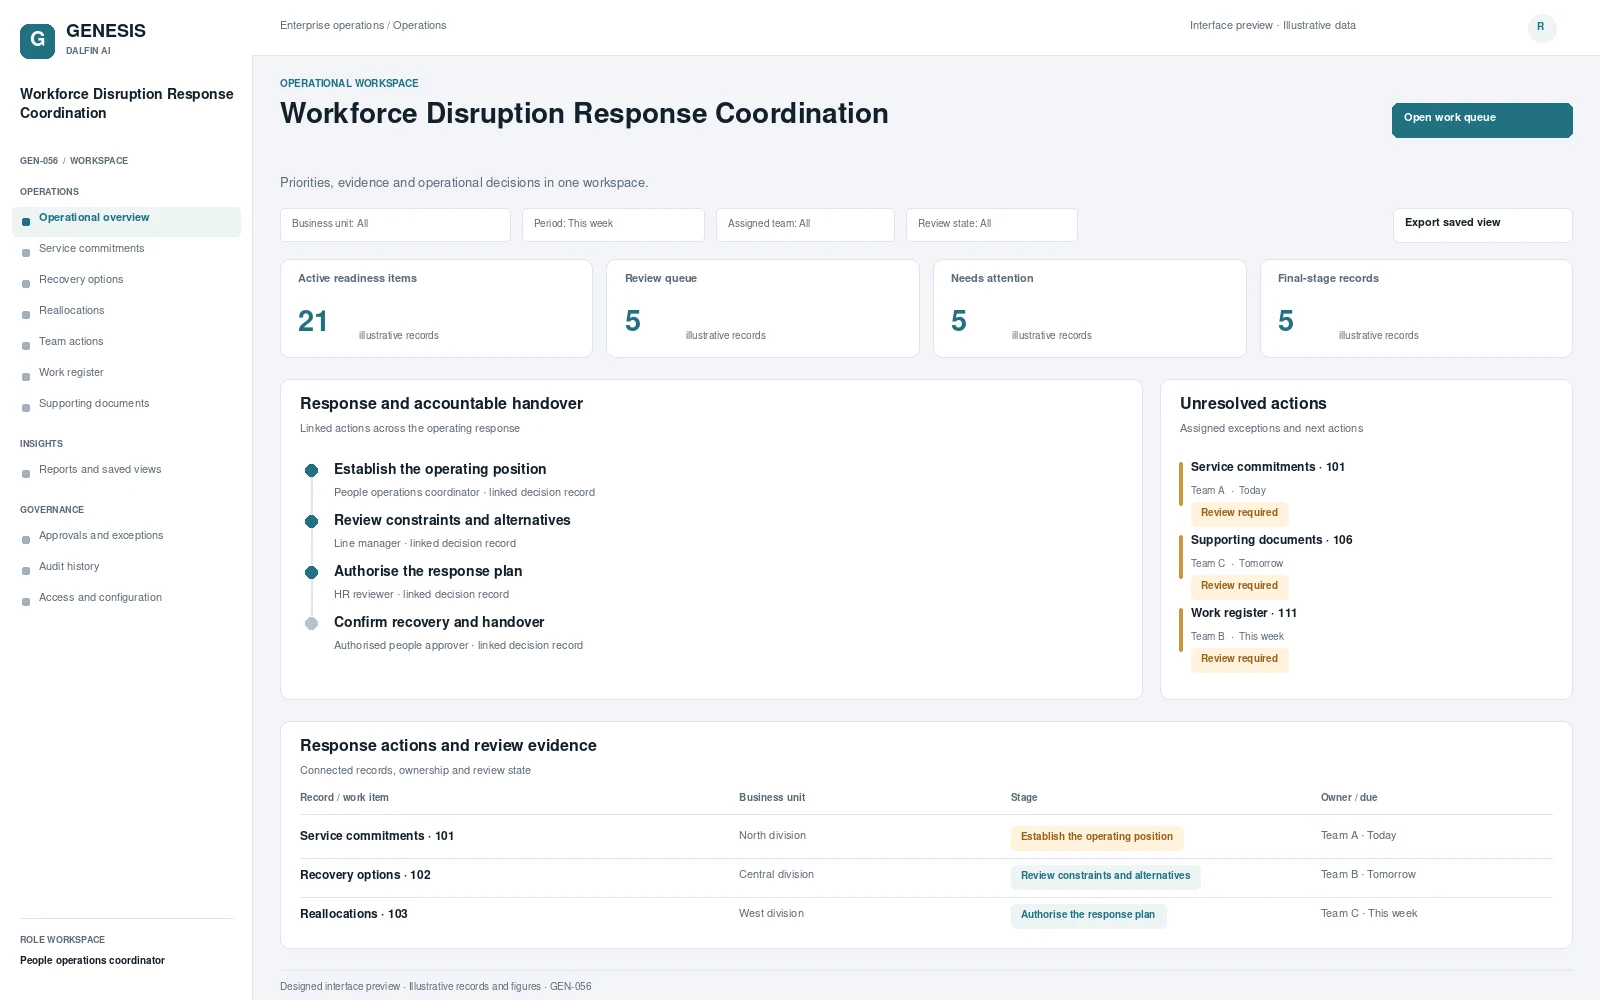 Interface preview
Coordinates the operational response to workforce disruptions affecting staffing and service commitments.
View blueprint →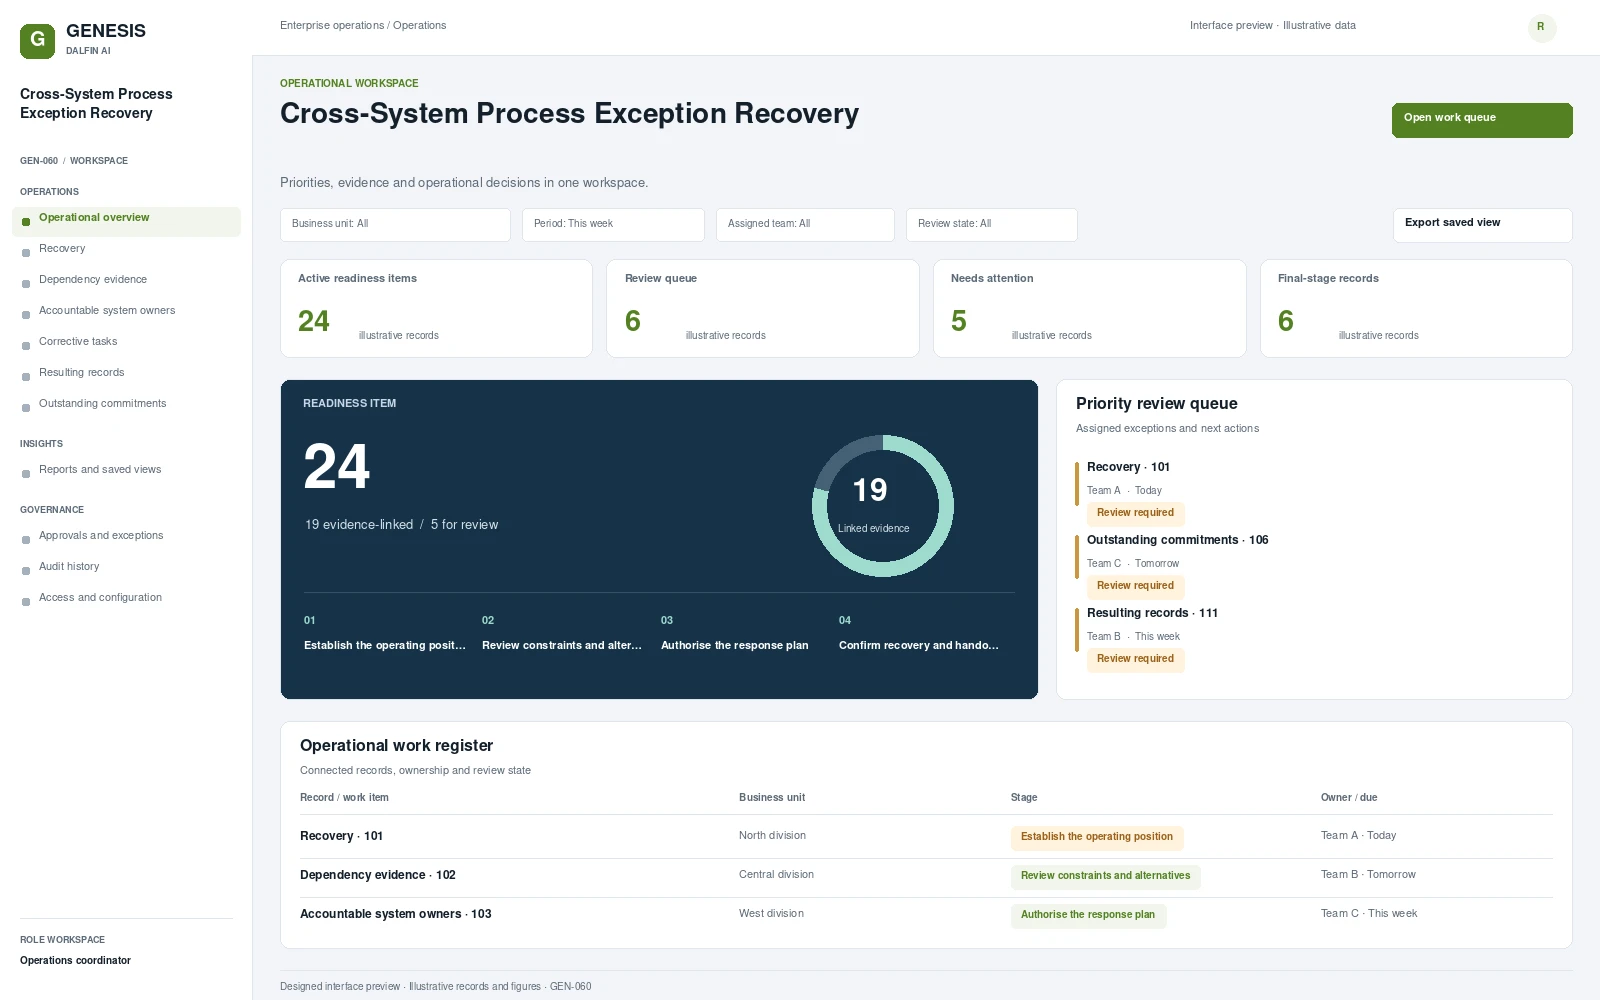 Interface preview
Coordinates recovery when a business transaction fails across connected systems.
View blueprint → Interface preview
Coordinate service intake, priority review, accountable ownership, approved fulfilment, restoration and reusable resolution knowledge.
View blueprint →